Sequoia pioneered the scouts model and many VC firms followed suit, but a consensus now seems to be forming that the model has reached limits in its current form.
German startup TimeTeller has developed a saliva test kit to help anyone understand their circadian rhythm; it aims to reduce side effects from cancer treatments.
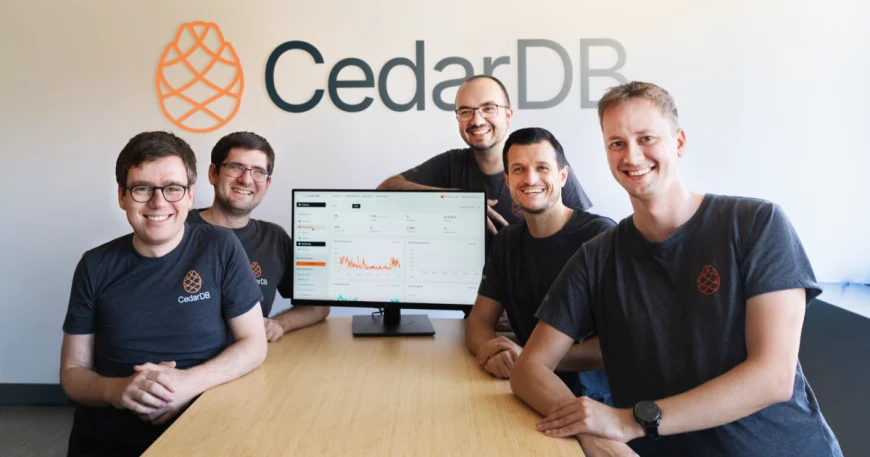
Databases have traditionally been designed either for analytical data or for operational data. But database engine CedarDB supports both, and its approach has gained relevance with the rise of agentic AI.
Cryptocurrency exchange Bitget revealed today that attackers who stole $387.5 million last week breached its systems after exploiting a zero-day flaw in third-party security products. According to Bitget, two separate investigations by blockchain security firm SlowMist and Google Cloud's cyber-defense arm Mandiant said the threat actors accessed Bitget's wallet environment after compromising two security appliances with zero-day exploits. After the breach, the attackers dropped web shells on one of the hacked appliances and malware on the crypto exchange's production wallet
The Clop ransomware gang has moved its data leak site to a new Tor address after confirming its previous server was compromised and defaced through an unpatched Grav CMS flaw that BleepingComputer has learned is an unauthenticated path traversal vulnerability. The Clop leak site was breached earlier this month by the ShinyHunters extortion gang, which first uploaded a small text file and later replaced the site with a full-page defacement displaying its Umbreon Pokémon logo and a link to its own data leak
D-Link warned customers of a maximum-severity vulnerability ( CVE-2026-86296) with public proof-of-concept (PoC) exploit code and no patch, affecting legacy DIR-822A dual-band Wi-Fi routers. This security flaw stems from a stack-based buffer overflow and improper data handling in the DHCP server component and can be exploited without authentication or user interaction. Attackers without valid credentials on the same local network can send crafted DHCP packets to the device, trigger the overflow, and potentially crash the DHCP daemon or achieve remote
The Florida Department of Highway Safety and Motor Vehicles (FLHSMV) has confirmed that its DAVID driver database suffered a data breach after the ShinyHunters extortion gang claimed to have compromised the system. The disclosure comes after the ShinyHunters extortion group claimed it breached the DAVID database and stole more than 200,000 driver records. "On September 4, 2026, FLHSMV learned of a data breach conducted by an international cybercriminal organization," the agency said in a statement posted to X. "The data breach
The three 28-year-old founders behind energy startup Furo moved from Silicon Valley and back to Germany, and yet secured $4 million in funding from mostly U.S. backers.