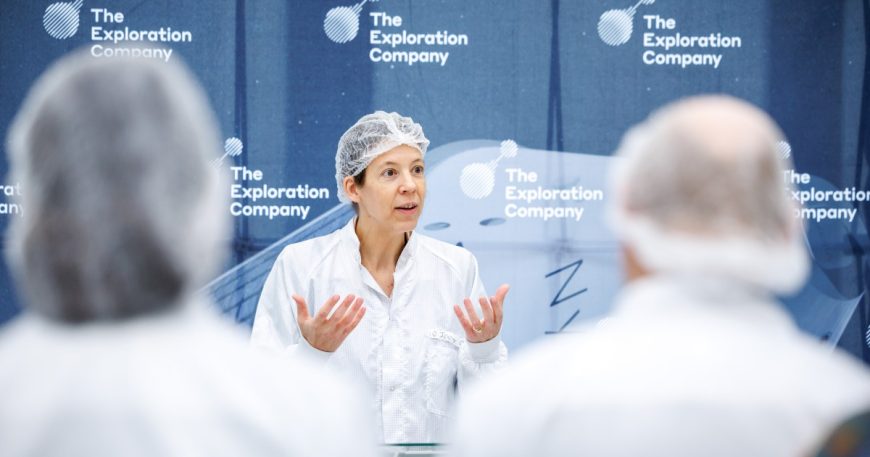
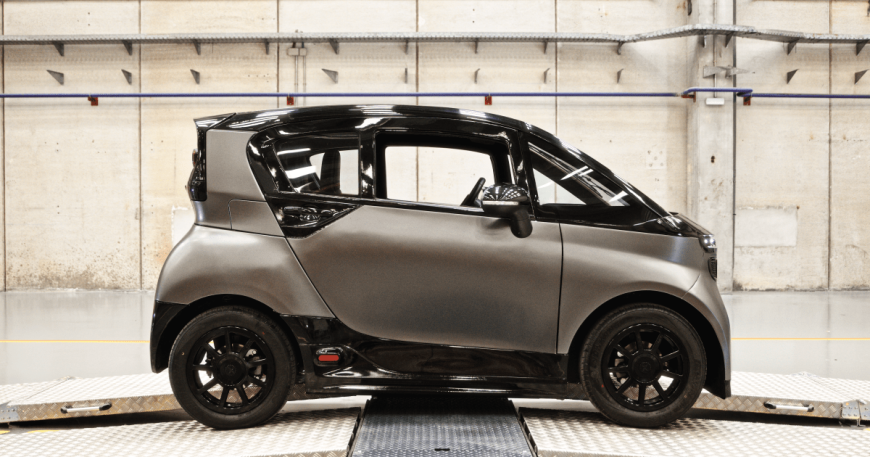
The Exploration Company (TEC) has raised $450 million to build reusable spacecraft, in what it describes as “the largest-ever Series C by a European space company.”
Attackers have begun targeting a critical-severity Citrix NetScaler flaw in the wild, according to vulnerability intelligence company Previdian. Tracked as CVE-2026-19490, this security flaw can allow unprivileged threat actors to bypass authentication remotely when the NetScaler appliance is configured as an AAA virtual server or as a Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy), depending on the NetScaler firmware version and whether SAML Action is configured. "We strongly recommend that customers review the official NetScaler ADC and NetScaler Gateway security
An SQL injection vulnerability in the All-in-One WP Migration and Backup plugin for WordPress could allow unauthenticated attackers to execute remote code and take control of affected websites. The plugin is used to back up, export, import, and move entire websites, including their databases, media, themes, and plugins, between servers or domains. The security flaw is tracked as CVE-2026-19949 and received a high-severity score. It was discovered by security researcher Jack Taylor, who reported it in mid-August through Defiant's cybersecurity