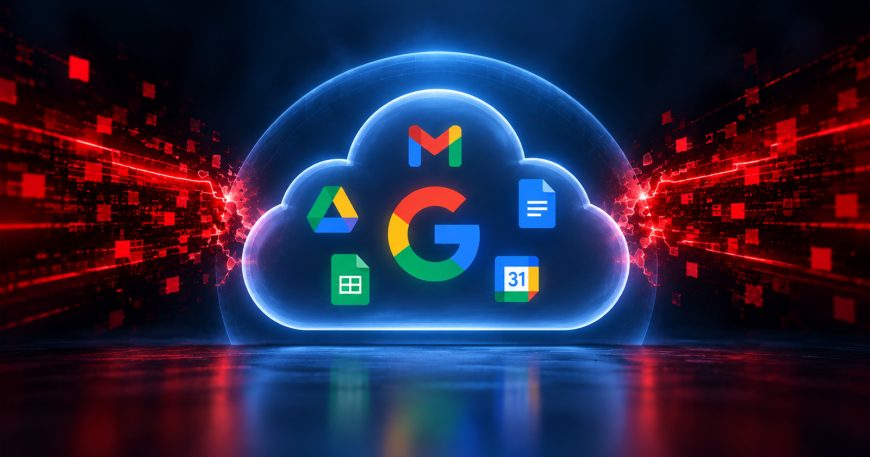
Google Calendar phishing campaign hijacks sessions, bypasses MFA
Since mid-August 2026, a phishing operation has been harvesting live Google sessions from corporate users. Every signal defenders usually rely on to judge a link returned a reassuring answer, and the operator built the chain that way on purpose. Material Security’s Threat Research team identified the campaign and has taken down hundreds of domains used by attackers in what they have dubbed Operation CloudFire. Here’s what they learned along the way. The lure: Google Calendar invites The messages arrive as